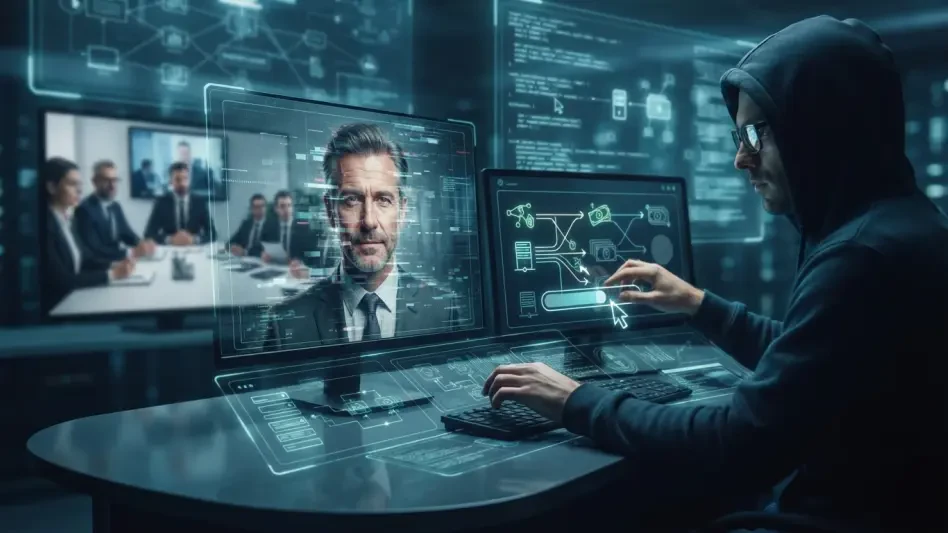
Financial institutions face a qualitative shift in social engineering as deepfake technology allows bad actors to simulate an executive’s likeness and voice during live video calls or meetings. This phenomenon marks a departure from traditional phishing attempts that relied on static images or poorly worded emails. Today, the precision of synthetic media allows criminals to manipulate the biological markers of identity that security teams once considered immutable. As we move through 2026, the global financial system finds itself at a crossroads where the cost of generating high-fidelity deception has plummeted while the potential for massive organizational loss has skyrocketed. This transformation is not merely a technological upgrade for criminals; it is a fundamental shift in the industrialization of fraud. By leveraging low-cost generative models, even relatively unskilled actors can now launch sophisticated attacks that previously required the resources of state-sponsored entities. The era of manual financial crime is fading, replaced by a reality where automation and scale define the new front line of defense.
The Mechanization of Deception
Scalability: The Democratization of Cyber-Attacks
In the recent past, executing high-level financial fraud required significant technical acumen and a specialized production team capable of manual exploitation. However, the current landscape in 2026 shows that open-source and affordable artificial intelligence tools have allowed fraudsters to clone voices and generate realistic digital personas with minimal effort. This democratization of sophisticated attack capabilities means that the barrier to entry has essentially vanished for novice bad actors. Professional criminal syndicates are no longer the only ones capable of conducting deep-level penetration; instead, a broader range of opportunistic individuals can now deploy high-fidelity assets. This shift has fundamentally changed the risk profile for banks and fintech firms, as they must now defend against a vastly more diverse set of adversaries. The accessibility of these tools ensures that the complexity of an attack is no longer a reliable indicator of the attacker’s resources or institutional backing.
The transition from manual, targeted strikes to mass-market automated campaigns represents a critical inflection point in the evolution of cyber-threats. By using AI to automate business email compromise (BEC), criminals can now bypass traditional rule-based filters that were originally designed to catch less sophisticated templates. These automated systems can target thousands of organizations simultaneously, tailoring each communication to the specific business context and writing style of the intended victim. This level of personalization at scale was historically impossible, yet it is now a standard feature of modern fraudulent operations. The sheer volume of these attacks forces organizations to contend with a constant barrage of highly personalized deceptions, where every single message carries the potential for a catastrophic breach. Consequently, the defense mechanisms of 2026 must pivot away from identifying known patterns and instead focus on the subtle deceptions that reveal the mechanical origins of corporate correspondence.
Deepfakes: The Erosion of Auditory and Visual Trust
Deepfake technology represents a profound qualitative shift in social engineering by exploiting deep-seated psychological triggers like trust and institutional urgency. Rather than merely impersonating an executive through text-based mediums, bad actors in 2026 can now simulate a leader’s physical likeness and vocal cadence during live video meetings or phone calls. This simulated credibility is particularly effective in today’s remote or hybrid work environments, where face-to-face verification is infrequent and employees are culturally conditioned to follow high-level executive requests without hesitation. When a subordinate sees and hears their CEO on a screen authorizing an urgent transfer, the psychological barrier to compliance is almost entirely removed. This manipulation of human judgment highlights a critical systemic vulnerability: the historical reliance on sight and sound as definitive proof of identity. As visual and auditory signals become easier to forge, the trust that underpins hierarchies is being weaponized against institutions.
Because many financial organizations still rely on verbal or visual confirmation to authorize high-value transactions, deepfakes allow fraudsters to bypass traditional security protocols with alarming ease. By projecting a trusted persona, criminals can convince even the most diligent employees to circumvent standard operating procedures under the guise of an emergency or a confidential deal. This tactic exploits the human element which remains the weakest link in the security chain, regardless of how much is invested in software firewalls. The ability to create a convincing digital double means that visual liveness is no longer a guarantee of authenticity. Furthermore, these attacks often occur during periods of high stress or transition, such as mergers or end-of-quarter reporting, where the pressure to perform overrides the instinct to verify. This sophisticated exploitation of organizational culture demonstrates that technical defenses are insufficient if they do not account for the emotional engineering techniques that deepfakes have mastered.
The Rise of Synthetic Identity and Systemic Gaps
The Sophistication: Synthetic Identity Fraud
Synthetic identity fraud involves a sophisticated process where criminals combine legitimate personal data with AI-generated elements to create entirely new, non-existent personas. This form of fraud is exceptionally difficult to detect because there is often no actual victim to report the crime, allowing the fraudulent account to remain silent during its initial stages of development. In the landscape of 2026, these Frankenstein identities are utilized to open accounts that appear perfectly legitimate to standard automated screening systems. Because the Social Security numbers used are often dormant or belong to individuals who do not monitor their credit, the fraud can persist for years without detection. This lack of a reporting party removes the traditional early warning system that banks have relied on for decades to flag identity theft. As a result, financial institutions are inadvertently fostering a growing population of shadow customers, each one a potential ticking time bomb that could result in significant losses.
Fraudsters are increasingly patient in 2026, using synthetic identities to build credible credit histories over several months or even years before executing a final bust out theft. During this seasoning period, these AI-enhanced personas maintain normal account activity, carry out small transactions, and ensure positive payment records, effectively blending in with the institution’s most reliable customers. This long-term strategy is designed to secure high credit limits and access to premium financial products. Furthermore, AI can now generate fraudulent documentation, such as utility bills or driver’s licenses, that mirror the security features of real documents with high precision. These sophisticated forgeries easily pass the static verification checks used during account onboarding, which often only look for visual consistency rather than forensic authenticity. The ability of these synthetic identities to mimic the lifecycle of a real consumer represents a systemic risk that threatens the data integrity of the credit ecosystem.
Weaknesses: Current Onboarding and KYC Protocols
Many financial institutions currently treat Know Your Customer (KYC) and identity verification as one-time events that occur only during the initial onboarding process. This static approach is fundamentally insufficient against AI-driven threats that evolve throughout the customer lifecycle and exploit the gaps between periodic reviews. In 2026, the reliance on a single point of entry for identity verification has become a major liability, as it assumes that an identity, once verified, remains untainted. Additionally, traditional liveness checks, such as asking a user to blink or move their head, are no longer foolproof. Modern software can map synthetic faces onto live movements in real-time, effectively spoofing these basic biometric tests with high accuracy. This technological leap has rendered many of the standard anti-spoofing measures obsolete, yet many institutions have been slow to upgrade their infrastructure. The gap between criminal capability and institutional defense continues to widen.
The industry recognized that because human security teams could not operate at the millisecond pace of an autonomous AI, organizations had to invest in their own AI-powered defensive layers to maintain a fighting chance. This shift necessitated a move toward zero-trust communication protocols, where no voice or video was accepted as authentic without secondary, out-of-band verification. Financial leaders established new standards for data sharing between institutions to flag synthetic identities before they could mature within the ecosystem. Specialized education programs were also deployed to train employees on the psychological markers of social engineering, bridging the gap between technical security and human awareness. These proactive measures transformed the defensive landscape from a reactive posture into a data-driven strategy that accounted for the total erosion of visual and auditory certainty. By fighting fire with fire, the financial sector successfully began to build a more resilient infrastructure capable of weathering the challenges.