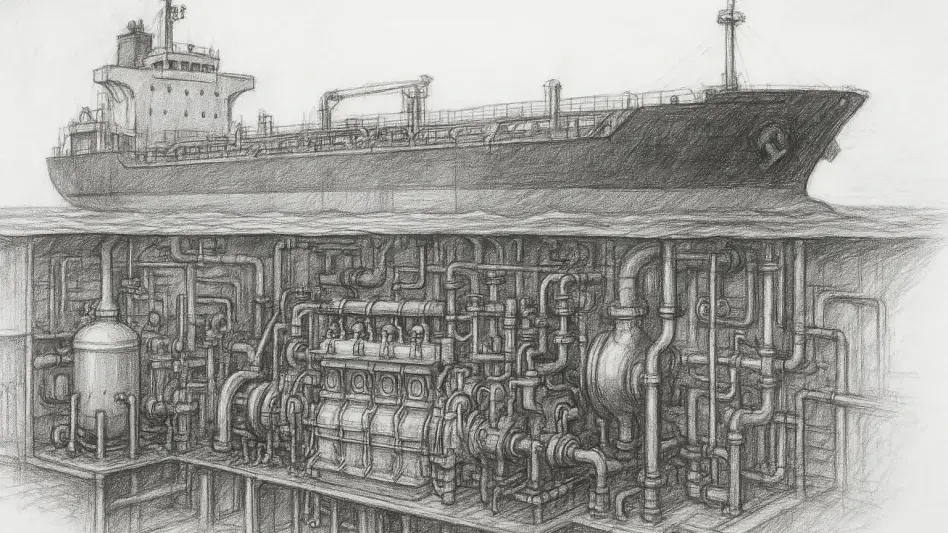
A 2024 malware campaign utilizing USB-borne remote access trojans demonstrated that machinery-monitoring and navigation systems on modern vessels are directly accessible to sophisticated hackers. This realization set the stage for the recent interventions in August 2026, when U.S. Coast Guard law enforcement, the FBI’s Cyber Action Team, and a USCG Cyber Protection Team boarded the 333-meter crude oil tanker VL Prosperity in the Atlantic. Carrying 2.3 million barrels of crude oil from Egypt’s Sidi Kerir terminal toward Galveston, the ship became the focus of a four-day forensic investigation after its network showed signs of compromise by a foreign actor. Just three days later, the 227-meter liquefied petroleum gas tanker Kohaku was similarly boarded in the Gulf of Mexico following a related suspected attack. These events occurred as both vessels transited critical chokepoints where traffic has intensified due to the disruption of access through the Strait of Hormuz. While official reports from the FBI and Coast Guard noted no physical damage or environmental impacts at the time, the potential for unauthorized access to propulsion and navigation systems underscores a growing vulnerability. The timing of these incidents coincides with a significant shift in U.S. maritime regulations, reflecting an urgent need for asset owners to bolster their defenses against high-consequence cyber incidents that target operational technology.
1. Formulate a Basic Inventory
Under federal regulations, specifically within the framework of 33 CFR 101.650, vessel owners must now maintain an exhaustive and precise inventory of every digital asset that communicates over a network. This requirement is not merely about counting laptops in the captain’s quarters; it involves a deep mapping of critical Information Technology (IT) and Operational Technology (OT) assets that manage the lifeblood of the ship. Each entry in the database must include the current software versions, firmware update histories, and specific hardware configurations for systems ranging from the Electronic Chart Display and Information System to the programmable logic controllers that regulate engine cooling and fuel delivery. Without this foundational clarity, it is impossible for operators to identify which systems are susceptible to the latest exploits or which components require urgent patching during a scheduled maintenance window. An accurate inventory acts as the primary defense against the unauthorized introduction of hardware, such as the rogue USB devices that have historically plagued maritime machinery networks.
The scope of this digital inventory extends significantly beyond the hardware physically owned by the shipping company, encompassing third-party and vendor-managed systems that are often overlooked in traditional security audits. Many modern tankers rely on specialized software for cargo monitoring, ballast water management, and emissions tracking that is maintained remotely by external contractors via satellite links. If a Cybersecurity Officer designates any of these outsourced systems as critical to the vessel’s safety or security, the underlying vendor relationship must be brought within the compliance boundary. This means that operators must now ensure that their service providers maintain the same level of transparency regarding software bills of materials and configuration management. This holistic approach ensures that a vulnerability in a contractor’s remote-access portal does not become a silent backdoor into the primary machinery-control networks of the entire fleet. By 2026, the integration of these vendor-managed assets into the core security inventory has become a mandatory step for any vessel seeking to maintain its operational license in U.S. waters.
2. Develop a Layered Network Architecture
In the lead-up to the 2027 enforcement deadlines, maritime operators are prioritizing the implementation of a layered network architecture that enforces strict segmentation between disparate functional zones. Historically, shipboard networks were often flat, meaning that a compromise in the crew’s recreational Wi-Fi could potentially provide a path to the vessel’s industrial control systems. To combat this, the new maritime cyber rules mandate the creation of intentional, robust boundaries between administrative IT environments and critical shipboard OT systems. This structural separation ensures that even if an office computer is infected with ransomware, the malware cannot easily jump to the propulsion or steering systems. Implementing this requires more than just a single firewall; it necessitates a comprehensive redesign of how data flows across the ship, ensuring that only authorized and verified traffic can transit the gap between the bridge and the engine room. Consequently, modern tankers are adopting software-defined perimeters that dynamically restrict access based on the specific role and location of the user.
Building a segmented architecture also involves securing the gateways that connect the vessel to the outside world, particularly the satellite internet links that have become ubiquitous in modern shipping. As seen in recent incidents involving GPS spoofing and electronic interference, external data inputs can be weaponized to feed false information into a ship’s navigation suite. By developing a layered defense, operators can implement sanity checks where navigation data is cross-referenced across isolated systems before being accepted as valid by the autopilot or dynamic positioning units. This multi-tiered approach ensures that a breach in one area—such as a compromised USB drive in a cargo terminal or a spoofed signal—is contained within a limited segment of the network. This containment prevents a localized digital error from cascading into a major grounding or collision, thereby protecting both the environment and the lives of the mariners on board. Furthermore, these architectural changes allow for more effective monitoring, as security teams can more easily spot anomalous traffic patterns crossing between supposedly isolated network segments.
3. Appoint a Qualified Cybersecurity Officer
One of the most significant shifts in the U.S. maritime regulatory environment is the requirement for every regulated facility and vessel to designate a Cybersecurity Officer (CySO). This role is fundamentally different from a traditional security officer found in a corporate setting, as it requires a deep, specialized understanding of both digital security and maritime operations. The CySO must be able to bridge the gap between the engine room and the IT department, translating technical vulnerabilities into operational risks that the ship’s master and owner can act upon. This individual is responsible for overseeing all security protocols, ensuring that the vessel remains in compliance with Coast Guard regulations, and acting as the primary point of contact during a suspected cyber incident. The designation of a CySO marks the transition of cybersecurity from a purely technical task to a core function of vessel management and maritime safety. This leadership role is essential for navigating the complex web of domestic and international regulations that govern the digital security of the global fleet.
Beyond technical oversight, the CySO is tasked with the critical responsibility of understanding how digital failures translate into physical consequences on the high seas. This means they must evaluate how a loss of data integrity in the cargo management system might lead to improper stability calculations or how a latency issue in the machinery-management network could affect emergency maneuvering. By having a dedicated officer who views cybersecurity through the lens of operational safety, shipping companies can ensure that their digital defenses are aligned with the physical realities of moving hazardous cargo. The CySO also leads the mandatory annual training programs for all personnel with system access, fostering a culture of cyber hygiene that is as rigorous as traditional firefighting or lifeboat drills. This leadership ensures that every member of the crew understands their role in preventing unauthorized access and responding to potential threats before they escalate. Such a human-centric approach is vital, as the crew remains the first line of defense against social engineering and physical security breaches.
4. Execute a Comprehensive Security Review
A cornerstone of the upcoming compliance milestones is the mandate for owners and operators to perform a thorough Cybersecurity Assessment of their entire operational landscape. This process is not a one-time checkup but a deep-dive analysis of all networks to pinpoint latent weaknesses in critical IT and OT systems that could be exploited by sophisticated actors. This involves active testing of network boundaries, reviewing the strength of access controls, and identifying any single points of failure in the vessel’s digital architecture. By systematically analyzing how an attacker might move through their systems, operators can prioritize their investments in security hardware and software. This assessment provides the data necessary to justify large-scale technical upgrades and ensures that the most vulnerable areas of the ship—such as the propulsion and fuel-oil systems—receive the highest level of protection and monitoring. It also helps in identifying legacy hardware that may no longer be supportable and represents an unacceptable risk to the vessel’s continued operation.
During the security review, the CySO must pay particular attention to identifying and mitigating Known Exploitable Vulnerabilities (KEVs) within the ship’s critical infrastructure. These are documented software flaws that are already being targeted by hackers in the wild, making them a high priority for remediation. The federal rules require that every KEV be either fixed or formally documented if the owner chooses to accept the risk. This documentation must include a clear rationale for why the vulnerability remains unpatched and what compensatory controls are in place to prevent its exploitation. In many cases, attackers do not need to develop custom exploits for a specific ship; they simply leverage unmitigated weaknesses in common software that have been left unaddressed. By focusing on KEVs, maritime operators can significantly raise the cost of entry for hackers, effectively closing the most common doors used by state-sponsored and criminal entities to gain a foothold on the network. This systematic elimination of low-hanging fruit is a highly effective way to reduce the overall risk profile of a commercial fleet.
5. Formalize and Submit a Protection Strategy
The culmination of the compliance journey is the creation of a formal Cybersecurity Plan, which must be reviewed and approved by the U.S. Coast Guard. This plan serves as the definitive operational roadmap for how a vessel or facility will maintain its security posture, respond to active threats, and recover from a potential breach. It is a living document that codifies the findings of the Cybersecurity Assessment and outlines the specific technical and procedural controls that have been implemented. Having an approved plan on file is a legal requirement for continued operation in U.S. waters, and it provides a standardized framework for inspectors to evaluate the readiness of a vessel. This formalization ensures that cybersecurity is no longer an ad-hoc effort but a structured, disciplined part of the vessel’s overall security management system, much like the physical security plans mandated after the implementation of the original MTSA in 2002. It also provides a clear chain of command for incident reporting, ensuring that the National Response Center is notified immediately of any significant digital threats.
A critical component of the protection strategy is the ongoing commitment to personnel training and the continuous adaptation to an evolving threat environment. The Cybersecurity Plan must detail how all crew members and land-based staff with system access will receive initial and recurring annual training to recognize phishing attempts, identify suspicious network behavior, and follow proper incident reporting procedures. As seen in the recent disruptions affecting tankers like the VL Prosperity and the Kohaku, the tactics used by digital adversaries are constantly shifting. Therefore, the plan must include mechanisms for regular reviews and updates to ensure that security measures remain effective against new forms of malware and electronic interference. By embedding cybersecurity into the daily operational routine of the fleet, the maritime industry can create a resilient front that protects the global economy from the growing threat of digital disruption on the high seas. This comprehensive strategy ensures that the entire organization—from the boardroom to the engine room—is aligned in its commitment to maintaining the safety and integrity of maritime commerce.
The coordinated response to the VL Prosperity breach demonstrated that a multi-agency approach was essential for securing maritime assets against sophisticated digital threats. Moving forward, vessel operators established a new baseline for safety by integrating cyber resilience directly into their traditional maintenance and operational cycles. The industry moved beyond simple compliance and began treating digital security as a core component of seaworthiness. Actionable next steps for shipowners involved the immediate audit of remote-access points used by third-party vendors and the acceleration of network segmentation projects to protect critical machinery. During 2026, the focus shifted toward real-time monitoring and rapid incident response, ensuring that crews were as prepared for a network compromise as they were for a mechanical failure. These efforts significantly reduced the risk of large-scale environmental disasters and protected the continuity of the global energy supply chain during a period of heightened geopolitical tension. This proactive stance ensured that vessels entering U.S. ports met the rigorous safety standards required for modern global commerce.