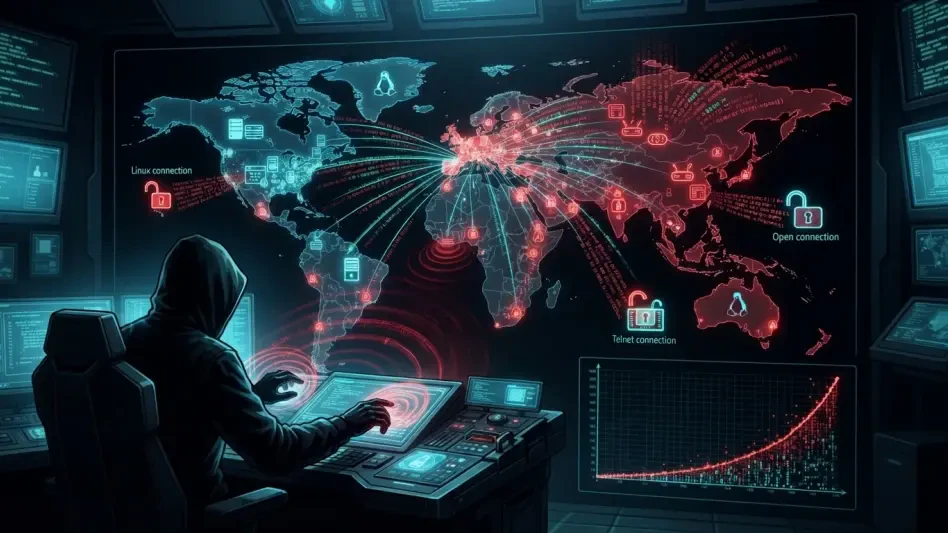
The operational simplicity of the Kairos botnet allows it to spread rapidly across Linux devices by executing basic shell commands once an unauthenticated Telnet session is established. This campaign represents a blunt yet effective approach to cybercrime, leveraging the Go programming language to create a portable and efficient toolkit for distributed denial of service activities. Unlike many contemporary threats that rely on elaborate social engineering or expensive zero-day exploits, Kairos returns to the basics of network exploitation by scanning for publicly accessible Telnet ports. Once a vulnerable target is identified, the botnet performs a series of automated checks and installations that transform the host into a willing participant in its malicious operations. This resurgence of legacy protocol exploitation underscores a persistent gap in the security lifecycle of embedded devices, where default settings remain a primary vector for large-scale infections. By focusing on the root user, the malware gains the highest possible privileges, ensuring it can manipulate system resources with total authority and minimal resistance in 2026.
1. Sequential Method of Initial System Compromise
The initial phase of the infection is surprisingly straightforward, beginning with the automated identification of exposed Telnet services that still utilize the default root username without any password protection. This oversight provides the attacker with an immediate and unrestricted gateway into the operating system. Once the session is established, the operator does not immediately deploy the payload; instead, they execute the uname -m command to carefully determine the processor architecture of the target machine. This step is vital for ensuring that the binary delivered is compatible with the underlying hardware, whether it be x86_64, ARM, or MIPS. By verifying these hardware specifications before the download begins, the botnet operator maximizes the success rate of the infection across a diverse range of devices, from enterprise servers to small consumer routers. This systematic approach allows the Kairos botnet to adapt to various Linux environments with high precision while ensuring that every successful login leads to a functional infection node.
After identifying the hardware architecture, the attacker moves to prepare the local environment for the incoming malicious file by switching to the /tmp directory, which is often writable by the root user. To ensure a clean installation and prevent conflicts with existing processes or previous infection attempts, the operator executes commands to delete any remnants of earlier malicious files. The retrieval of the malware itself is a multi-stage fallback process designed to bypass various network restrictions or missing system utilities. The system attempts to download the payload using a sequence of common tools including wget, curl, and BusyBox wget, eventually falling back to TFTP if the more standard web-based utilities are unavailable. Once the download is successfully completed, the malicious binary is granted full permissions through the chmod 777 command and is immediately executed to run in the background, completing the initial compromise and establishing the malicious process within the volatile memory of the host device.
2. Internal Botnet Behavior and Connection Storms
Once the Kairos malware is active on a host, its primary objective is to maintain a persistent and reliable communication channel with its designated command-and-control server. The bot initiates this process by sending a plain-text registration beacon that includes the device architecture and processor count, followed by a blank line transmitted every two seconds to keep the network socket open. This heartbeat mechanism ensures that the operator can issue attack commands at a moment’s notice. When an attack is initiated, the malware demonstrates its resource-intensive nature by spawning a massive number of worker threads. Specifically, the bot creates 128 separate worker threads for every CPU core detected on the system, with a minimum threshold of 256 threads. This aggressive parallelization is designed to leverage the full computational power of the compromised device, turning even relatively low-powered hardware into a significant source of outgoing network traffic that can be coordinated with thousands of other infected nodes globally.
The actual attack mechanism utilized by the Kairos botnet is characterized by a connection storm rather than a traditional high-volume traffic flood. Each spawned worker thread performs a standard TCP handshake with the victim’s server, then sends a single space character every five seconds to prevent the connection from timing out. By holding thousands of these legitimate connections open simultaneously, the botnet rapidly exhausts the available socket capacity of the target service, effectively blocking genuine users from accessing the resource. To avoid detection by system administrators during this phase, the malware attempts to hide its presence by renaming its process to [kworker/0:1], which mimics the naming convention of a standard Linux kernel thread. While this camouflage might deceive a casual observer using basic monitoring tools, the underlying network activity and the actual process ID remain visible within the /proc directory, providing a clear trail for diligent investigators who are trained to look beyond superficial process names.
3. Strategic Defensive Actions for Enhanced Security
Protecting against the Kairos botnet required a return to fundamental security practices that many organizations had previously neglected in their edge deployments. Security teams found that the most effective first step was the complete deactivation of the Telnet protocol, replacing it with encrypted and authenticated methods such as SSH. For systems where legacy services could not be entirely disabled, administrators enforced strict credential policies that prohibited the use of default login information and eliminated accounts with blank passwords. Furthermore, network-level defenses were strengthened by implementing firewall rules that blocked all outbound traffic to known malicious IP addresses on the specific ports used by the botnet, such as 8080 and 9999. These proactive measures significantly reduced the attack surface and prevented compromised devices from successfully registering with their command-and-control servers, thereby neutralizing the threat at the network perimeter before it could participate in larger coordinated denial of service campaigns.
Beyond immediate remediation, long-term security strategies involved the integration of signature-based detection and continuous process auditing. Security professionals deployed Intrusion Detection System rules specifically tuned to flag the unique plain-text registration beacons and the frequent heartbeat signals emitted by the malware. They also utilized YARA rules to scan local file systems for the specific Go-based signatures associated with different versions of the Kairos binary. Monitoring efforts were redirected to identify unusual kernel worker processes that maintained an excessive number of outbound network connections, which served as a clear indicator of a hidden infection. Moving forward, the focus shifted toward the implementation of zero-trust architectures for IoT and embedded devices, ensuring that no internal service is reachable without explicit authentication. These efforts collectively fostered a more resilient infrastructure capable of withstanding the persistent threat of automated botnets while providing a blueprint for securing the next generation of connected devices.