In Uganda, specialized police units dismantled transnational fraud rings that used sophisticated call centers to execute pension and investment scams. This specific intervention formed a critical component of a much larger, pan-African law enforcement initiative known as Operation Serengeti III. Orchestrated by INTERPOL between June and August of this year, the operation mobilized 21 different nations to confront the burgeoning digital threats that have plagued the continent. Unlike previous efforts that focused on individual threats, this massive undertaking aimed at the very heart of the criminal infrastructure, resulting in the apprehension of over 1,400 suspects. The scale of the problem was laid bare as investigators uncovered a web of exploitation that affected more than 65,000 victims worldwide. By synchronizing local police power with international intelligence, the operation successfully disrupted nearly 11,000 malicious networks. This effort marks a vital shift in how nations collaborate to secure digital borders.
Infrastructure Neutralization: Targeting Regional Criminal Hubs
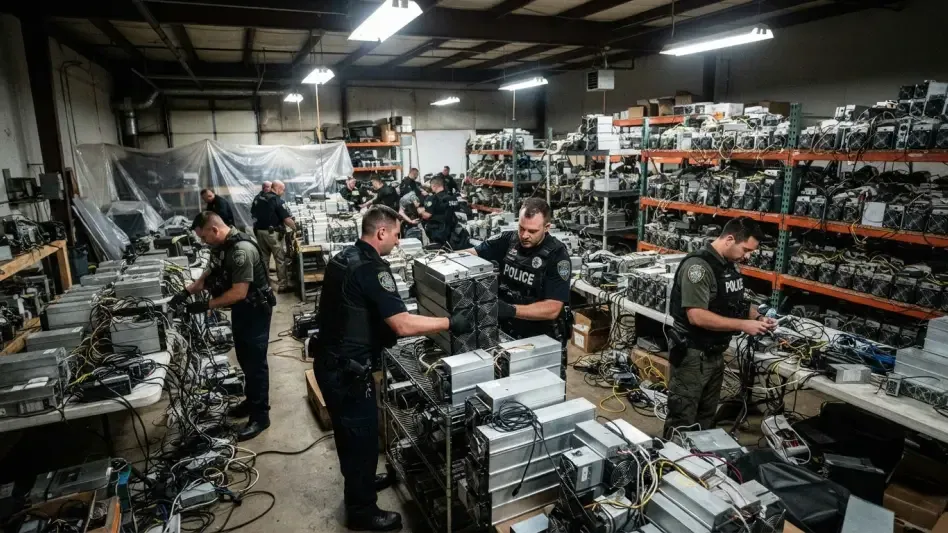
In Angola, the tactical focus shifted from digital footprints to the physical architecture that sustains modern cybercrime. Law enforcement officers executed high-stakes raids that resulted in the seizure of more than 2,000 cryptocurrency mining devices. These machines were not merely hobbyist setups; they were powered by six illegal industrial-scale transformation stations, which were valued at well over $1 million. This specialized hardware allowed criminal syndicates to launder illicit funds and generate untraceable capital while placing an immense strain on the local power grid. By targeting these physical nodes, the operation did more than just stop a few transactions; it physically dismantled the foundation required for sustained high-tech theft. This strategy highlights a growing realization among investigators that cybercrime is often anchored in real-world utility theft and hardware hubs. Neutralizing these assets effectively raises the overhead costs for criminals, making it far more difficult for them to restart operations once a raid concludes.
Nigeria emerged as another vital theater of operations where the emphasis was placed on dismantling technical fraud structures. One of the most significant arrests involved an individual suspected of managing a massive phishing and business email compromise campaign. This operation was staggering in its reach, utilizing a database of over 2.1 million email addresses to bait potential victims. The suspect facilitated the laundering of millions of dollars by converting stolen currency into various digital assets, showcasing the sophisticated intersection of traditional fraud and modern blockchain technology. Beyond this single arrest, the Nigerian authorities worked to trace the complex financial trails that link local operatives to international money laundering rings. This investigative work allowed the task force to map out how stolen funds flow through different jurisdictions, providing a clearer picture of the financial plumbing of modern syndicates. Such detailed intelligence is crucial for preventing the resurgence of these groups in the future.
Collaborative Defense: Synergy Between Private and Public Sectors
A defining characteristic of Operation Serengeti III was the unprecedented level of cooperation between public law enforcement and private-sector cybersecurity firms. Organizations like Group-IB and Team Cymru provided the technical backbone for the operation by sharing critical intelligence on phishing kits, botnets, and command-and-control servers. This data allowed police to identify the digital fingerprints of criminal groups before they could even launch their next wave of attacks. By mapping out the interconnected systems used by these syndicates, investigators were able to link disparate local crimes to centralized criminal hubs. This collaborative model demonstrates that the most effective way to combat borderless digital crime is through a borderless sharing of technical resources and expertise. The synergy between private analysts, who possess deep technical insights, and public officers, who hold the authority to make arrests, created a formidable barrier against cyber exploitation. This partnership effectively shortened the time between detection and intervention.
The conclusion of Operation Serengeti III provided a clear blueprint for the future of digital defense across the African continent. Looking back at the achievements, the synthesis of real-time threat intelligence and international coordination proved to be the most effective deterrent against complex criminal syndicates. Moving forward, the most vital step involves the institutionalization of information-sharing protocols established during these raids. To maintain this momentum, nations must prioritize the training of specialized cyber units and the harmonization of legal frameworks to ensure cross-border evidence is admissible. This operation demonstrated that recovered assets, which exceeded $105 million, could be redirected toward bolstering national infrastructures. Policymakers should now focus on creating permanent regional centers for cyber excellence that operate year-round. By shifting toward proactive defense and systemic resilience, participating nations created a more secure environment, proving that protecting communities required shared technical excellence.