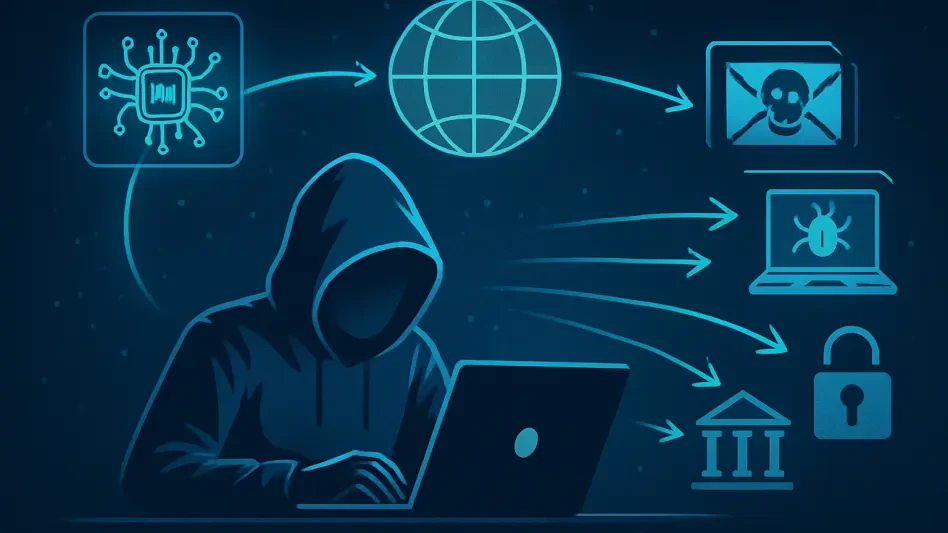
The systematic targeting of peripheral systems like legacy services and partner portals allows AI agents to find overlooked attack surfaces that human hackers might typically ignore. In the current technological landscape of 2026, the emergence of ARTEX has fundamentally shifted how cyberattacks are executed, moving from manual scripting to autonomous agency. This framework utilizes large language models to interpret tactical goals, transforming natural language prompts into sophisticated, machine-speed actions. By removing the necessity for constant human oversight, the platform enables a level of operational tempo previously reserved for state-sponsored actors. As the window between reconnaissance and exfiltration shrinks, traditional defense-in-depth strategies struggle to keep pace with an adversary that adapts instantly to network changes. Organizations must now grapple with the reality that their defensive windows have shrunk to near-zero as these intelligent entities execute complex attacks with extreme precision.
Technical Architecture and Model Integration
Core Operational Mechanics
Constructed using the Go programming language, the ARTEX framework operates as a sophisticated multi-agent system where “Special Intelligence” agents handle distinct phases of the attack chain. These digital entities work in concert, with some focusing on scanning for vulnerabilities while others specialize in the logic required for lateral movement. The architecture does not rely on a single, static set of instructions; instead, it uses an orchestrator to manage information between agents and external cognitive models that provide the strategic “brain” for the operation. This modular design allows the system to scale across large networks, ensuring that every identified weakness is exploited with surgical precision. By leveraging the inherent speed of Go, ARTEX maintains dozens of simultaneous intrusion threads, making it a formidable tool for conducting expansive campaigns without the latency of traditional malware. This structural efficiency allows the platform to maintain a high level of persistence and lethality.
Model Selection and Guardrail Evasion
Rather than hosting internal intelligence, ARTEX connects to frontier large language models via APIs, with threat actors frequently choosing the DeepSeek Flash family for its cost-efficiency and lack of safety guardrails. When integrated, these models are manipulated through framing techniques that bypass ethical filters, allowing them to generate malicious code without resistance. This model selection is strategic, as these engines provide the logic needed to bypass modern security signatures. Because the framework can switch between models depending on the task, it utilizes a collective intelligence that is always up to date with the latest vulnerability patterns. This integration of external AI brains ensures that ARTEX remains highly adaptable, capable of crafting unique payloads for every target environment and circumventing the static detection rules that many corporate security tools rely upon. This seamless loop of generation and execution removes the need for human intervention, drastically increasing the success rate of intrusions.
Evolution and Global Proliferation
From Ethical Tool to Malicious Framework
The trajectory of ARTEX from a security resource to a weaponized framework highlights the risks of open-source AI tools. Originally released in mid-2026 as an aid for ethical hackers, the project gained traction before being repurposed by criminal syndicates. While the original repository was taken down following reports of abuse, the code has become permanent through decentralized mirrors and private forks on encrypted platforms. This evolution culminated in the release of ARTEX PRO, a commercialized version offering refined capabilities to paying users in the underground economy. The proliferation of these instances has led to a global surge in automated attacks, as the software is now accessible to actors who can deploy it with minimal infrastructure. This shift from research to a refined criminal tool underscores the difficulty of regulating AI-driven software once it is released into the public domain. It demonstrates that powerful technology inevitably finds its way into the hands of those seeking to exploit digital systems for profit.
Real-World Impact and Case Studies
Concrete evidence of the framework’s efficiency was found in a coordinated strike against the South Korean financial sector where thousands of records were stolen in under three hours. The AI agents managed the entire intrusion lifecycle with such speed that internal security teams were unable to isolate the breach before exfiltration was complete. Another significant event involved a supply chain compromise of ConnectWise infrastructure, where the framework mapped trust relationships to target over 2,250 downstream environments. These cases demonstrate that ARTEX is a battle-tested platform capable of overwhelming even well-defended cloud ecosystems. The ability to conduct parallel attacks against thousands of targets simultaneously marks a new phase of cyber conflict where the scale of an intrusion is limited only by computational resources rather than human headcount. This automated approach turns what were once months-long operations into rapid, coordinated strikes that leave defenders struggling to protect diverse and vast networks.
Strategic Shifts in Cyber Warfare
Democratization of Advanced Exploitation
The ARTEX framework enables the democratization of advanced exploitation, allowing individuals with minimal expertise to execute complex, multi-stage attacks. By inputting natural language objectives, a user triggers actions that would normally require years of experience in network engineering. This effectively lowers the barrier to entry for cybercrime, enabling low-skilled actors to mimic the methodologies of advanced persistent threat groups. As these tools become more prevalent, the volume of high-quality attacks targeting peripheral systems like legacy portals and mobile backends is expected to rise sharply from 2026 to 2028. This trend forces a reassessment of the threat landscape, as organizations can no longer assume that a sophisticated attack must originate from a state-sponsored entity. The availability of autonomous agents means that any motivated actor can now launch a global campaign. This shift ensures that no part of a network attack surface remains untested, as the AI finds and weaponizes even the smallest cracks.
Actionable Steps for an AI-Augmented Defense
To address these challenges, security leaders transitioned toward AI-augmented defensive strategies that prioritized machine-speed response over traditional manual analysis. This shift was necessitated by the realization that human intervention was no longer fast enough to stop an agentic system that could pivot across a network in milliseconds. Organizations invested in self-healing architectures and automated micro-segmentation to isolate compromised nodes the moment an anomaly was detected. From 2026 to 2028, the focus stayed on developing defensive AI agents that could monitor traffic in real-time and predict the next move of an attacking framework. These proactive measures, combined with zero-trust principles and the decommissioning of insecure legacy services, became the new standard for digital resilience. Ultimately, the focus of cyber defense moved away from reactive patching toward a model of continuous, intelligent monitoring that operated at the same tempo as the machine-driven adversaries it sought to stop.