The successful seizure of five central servers effectively silenced the primary communication and extortion channels used by this prolific ransomware collective. This decisive action, part of a multi-national effort known as Operation KillSwitch, represents a watershed moment in the global fight against organized digital extortion. For months, the KillSec collective operated with relative impunity, leveraging a decentralized command structure and advanced encryption to target more than 280 organizations across the globe. The coordination required to neutralize such a sophisticated threat involved the synchronization of law enforcement efforts across Spain, Greece, Romania, and the United Kingdom, alongside the technical support of the FBI. By systematically targeting the digital backbone of the organization, authorities did more than just arrest key individuals; they dismantled the very tools used to facilitate large-scale financial theft. This operation underscores the shifting nature of digital crime, where borders provide no sanctuary for those who exploit the anonymity of the internet to cause widespread economic disruption.
Youthful Leadership: The Challenge of Teenage Cybercrime
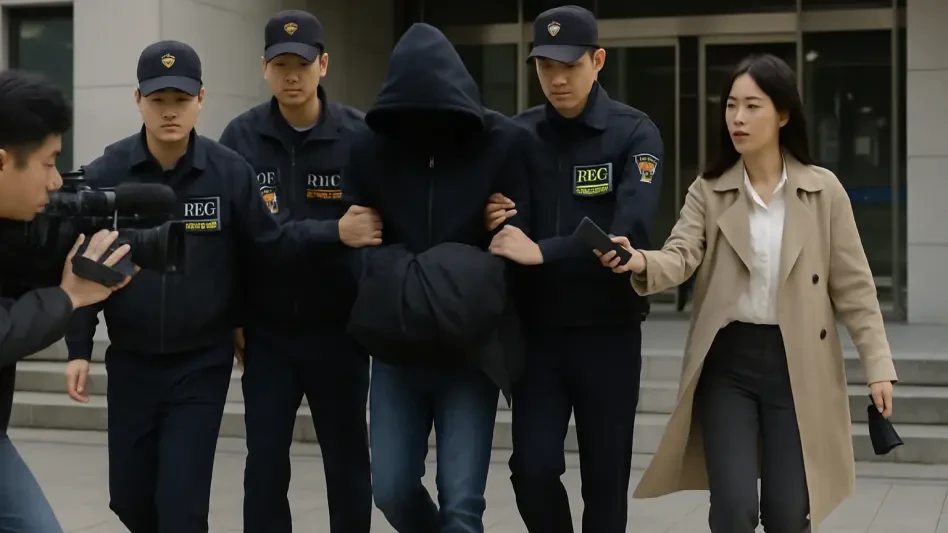
One of the most startling revelations from the investigation was the profile of the individuals orchestrating the criminal enterprise. In Alicante, Spain, authorities apprehended a 16-year-old Romanian national believed to be the primary administrator of the entire KillSec network. Despite his age, this individual allegedly managed a complex operation involving encrypted communications, anonymization tools, and the oversight of a global affiliate network, challenging the traditional image of high-level cybercriminals. The investigation, which began in 2025, also identified other young collaborators, including a developer who only recently reached the age of majority. This trend indicates a lowering barrier to entry for sophisticated cybercrime, as younger, tech-savvy individuals leverage their skills to cause massive economic disruption. The ability of a minor to lead a group responsible for hundreds of successful breaches demonstrates the growing challenge law enforcement faces in tracking a new generation of digital natives who see cyber-extortion as a viable career path.
The Spanish component of the probe, dubbed Operation ROTOMA, began as a joint effort between the Guardia Civil and the FBI’s San Juan Field Office. Investigators initially identified the suspect through a single profile image, eventually tracing his physical location to a residence and hotel office in Alicante. A second individual, a woman, is also under investigation in Spain for her potential connection to the group’s activities. Furthermore, the investigation identified a suspected developer for the group who only recently reached the age of majority, having been a minor during many of the alleged offenses. This trend underscores a growing consensus among security experts: the barrier to entry for high-stakes cybercrime is lowering, with younger individuals leveraging high-level technical skills to cause massive economic disruption. Law enforcement must now adapt its strategies to address a demographic that is technically proficient but may not fully grasp the legal consequences of their digital actions in the global landscape.
Technological Warfare: AI Integration and Modern Extortion
KillSec’s operational methodology stood out for its integration of cutting-edge technology, specifically the use of artificial intelligence to streamline their illicit activities. The group utilized AI to automate infrastructure maintenance and to more efficiently profile high-value targets, allowing a small core team to operate with the reach of a much larger organization. This evolution in cyber-extortion marks a significant shift, as bad actors weaponize emerging technology to increase the scale and velocity of their attacks. By deploying machine learning algorithms to identify software vulnerabilities, the group could execute reconnaissance at speeds that human operators could never match. This automation allowed them to maintain a persistent presence across multiple networks simultaneously, ensuring that their pipeline of potential victims remained full. The integration of AI suggests that the next generation of ransomware threats will be defined by their ability to adapt and respond to security measures in real-time.
The group primarily targeted vulnerabilities in cloud storage environments to gain unauthorized access to sensitive networks. Once inside, they employed a double extortion model: stealing vast amounts of data before encrypting local files. Victims were then threatened with the public release of their information on a dedicated leak site if a cryptocurrency ransom was not paid. This strategy ensured that even if a company could restore its systems from backups, the threat of a data breach remained a powerful lever for extortion. This approach bypasses traditional disaster recovery plans that focus solely on uptime, forcing executives to weigh the cost of a ransom against the potential for catastrophic reputational damage and legal liability. Furthermore, by focusing on cloud environments, KillSec exploited the often-misunderstood shared responsibility model, where users frequently leave sensitive buckets exposed or misconfigured. This tactical focus allowed the group to bypass traditional perimeter defenses and strike directly at the core.
Global Impact: Assessing the Damage and Technical Seizures
The scale of KillSec’s activity was immense, with an estimated 1,000 attempted attacks resulting in over 280 confirmed victims. The financial consequences were severe, evidenced by a single attack on a Catalan organization that caused over €1 million in damages. This specific case provided the crucial evidence needed to link the Spanish-based administrator to the broader international network, eventually leading to the seizure of five central servers and the redirection of the group’s web domains. These financial losses extend beyond the immediate ransom demands, encompassing the costs of forensic investigations, legal fees, and long-term loss of consumer trust. Each successful breach served as a proof of concept for the group’s efficiency, attracting more affiliates and increasing the frequency of their operations. The cumulative economic impact across the 2026 fiscal year alone highlights why ransomware has transitioned into a top-tier national security priority for governments across the European Union and North America.
The dismantling of KillSec established a new standard for how international coalitions managed the intersection of juvenile justice and high-tech crime. Security professionals recommended that organizations moved beyond traditional firewall protections to adopt zero-trust architectures that verified every access request, regardless of its origin. This shift was necessary because the investigation proved that even minors could bypass sophisticated perimeter defenses using stolen credentials or AI-assisted social engineering. Experts emphasized the importance of regular data backups and the implementation of robust encryption for all sensitive data at rest to mitigate the impact of double extortion tactics. Furthermore, the collaboration between the public and private sectors demonstrated that sharing threat intelligence in real-time was the most effective way to neutralize emerging threats. The operation served as a reminder that while the tools of the trade shifted toward automation, the human element remained both the greatest vulnerability and the strongest line of defense.