The chilling reality of modern asymmetric warfare became clear when an invisible adversary attempted to weaponize the very cooling systems designed to preserve the lifeblood of the French medical system. When the clock struck midnight on November 1, 2024, a silent digital intrusion threatened to destroy the vital medical reserves of the Établissement français du sang (EFS). In an age where hackers often hunt for financial data or sensitive passwords, this sophisticated group chose a visceral target: the thermostats. By infiltrating the refrigeration control systems, these cyber-saboteurs attempted to cook frozen plasma by remotely hiking storage temperatures from a frigid -30°C to a scorching 110°C. This incident marked a chilling shift in the landscape of digital conflict, moving from the theft of data toward the direct manipulation of the physical world.
A Midnight Digital Siege: Protecting Life-Saving Supplies
The attackers executed their plan with surgical precision, targeting the specific logic controllers that regulate industrial cooling. By overriding the safety parameters of the EFS storage units, the hackers sought to induce a rapid thermal surge that would have coagulated proteins and rendered life-saving plasma completely inert. This was not a random act of digital vandalism; it was a calculated attempt to disrupt a nation’s medical readiness. The breach demonstrated that even the most mundane operational hardware, such as a refrigeration unit, can be transformed into a weapon if it is connected to a network without sufficient isolation.
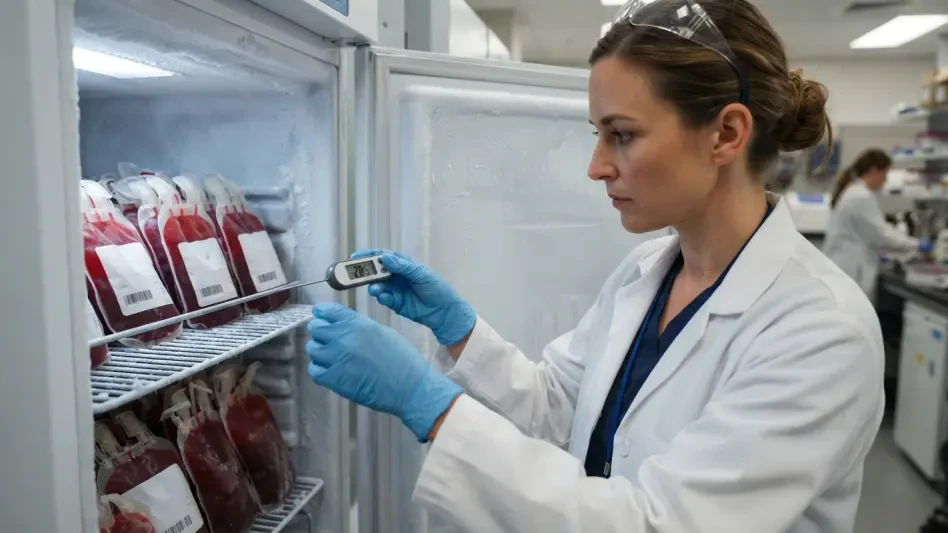
Fortunately, the digital siege met its match in the form of redundant hardware fail-safes. While the attackers successfully manipulated the software interface, they could not bypass the physical sensors that triggered local, non-networked alarms. These sirens alerted facility staff who were physically present, allowing them to intervene before the thermal energy could overcome the insulation of the storage vats. This incident proved that while the digital layer of an organization is vulnerable, a multi-layered defense strategy that includes physical oversight can provide the necessary buffer to prevent a total catastrophe.
The High Stakes: Protecting the National Blood Supply
The EFS is not merely a government agency; it functions as the central nervous system of the French healthcare network. It maintains the responsibility for collecting, storing, and distributing blood and plasma used in emergency surgeries and the manufacturing of specialized medicines. In the specialized field of cryopreservation, temperature stability is quite literally a matter of life and death, as even a brief fluctuation can render biological samples and transfusable products useless. This attack highlighted a growing trend of targeting critical infrastructure where the primary goal is the systematic sabotage of essential public services.
As supply chains have become increasingly digitized between 2026 and 2028, the vulnerability of medical infrastructure serves as a reminder that physical health is inextricably linked to digital firewalls. The national blood supply is a finite and precious resource, often reliant on the altruism of millions of donors. Sabotaging this supply does more than just destroy physical inventory; it erodes public trust in the healthcare system’s ability to protect the most basic elements of life-saving care. Consequently, the defense of these reserves is now viewed as a matter of national security rather than a simple IT concern.
Anatomy of the Attack: From Remote Software to Thermal Targets
Investigation revealed that the breach originated through a third-party refrigeration supplier’s remote-monitoring software rather than the internal network of the EFS. By exploiting a vulnerability in a component used by the vendor Coolworld, the attackers gained the ability to rewrite the operational logic of the cooling units across multiple locations. They aggressively adjusted defrost thresholds and temperature setpoints, aiming to trigger a catastrophic failure of the cold-storage environment. This “supply chain” approach to hacking allowed the perpetrators to bypass the EFS’s primary security perimeter by piggybacking on the trusted access granted to a maintenance partner.
However, the attempt was neutralized by a combination of high-tech redundancy and old-fashioned human vigilance. Independent alarm systems, which operated outside the compromised software, immediately alerted on-duty technicians to the anomalies as they occurred. This allowed staff to execute manual overrides and relocate sensitive materials to backup units, ensuring that not a single vial of plasma was lost and that nationwide distribution remained entirely uninterrupted. The failure of the attack underscored the importance of maintaining an air gap between management software and the emergency shutdown systems that protect physical assets.
Expert Analysis: The Evolution of Cyber-Sabotage
Cybersecurity specialists from firms like Ridge Security and Xcape, Inc. noted that this incident reflected a “near-miss” that mirrored previous attacks on European food retailers. While those earlier attacks successfully forced businesses to discard massive quantities of spoiled food, the EFS incident demonstrated a superior level of defensive resilience. Experts pointed out the critical distinction between a hacker changing a digital setpoint and actually achieving a physical state change in the environment. Because the EFS maintained “human-in-the-loop” monitoring, the digital command never had enough time to manifest as physical heat that could damage the biological cargo.
The consensus among the security community is that this event serves as a definitive case study in why operational technology (OT) requires greater security rigor than traditional IT systems. Unlike a data breach where information is copied, an OT breach can lead to the permanent destruction of physical assets. Specialists emphasized that the focus of modern security must shift toward protecting the integrity of commands sent to hardware. As medical facilities continue to integrate internet-connected devices, the EFS experience has become a foundational lesson in balancing the convenience of remote monitoring with the necessity of manual control overrides.
Hardening Critical Infrastructure: Managing Third-Party Risks
To address these threats, organizations implemented strict network segmentation that isolated refrigeration and HVAC controls from the broader internet. Third-party software used for remote maintenance became subject to multi-factor authentication and rigorous access filtering to prevent unauthorized manipulation of thermal setpoints. The EFS success story demonstrated that physical redundancies, such as independent hardware alarms and documented manual intervention protocols, were the final line of defense. By treating every internet-connected device as a high-priority asset, the service protected its operations against the rising tide of digital sabotage.
The incident ultimately fostered a new standard for infrastructure resilience that prioritized human intervention over total automation. Administrators realized that the most effective way to safeguard medical supplies was to ensure that no single digital vulnerability could result in a physical failure. This shift in strategy included the deployment of analog backup thermometers and the training of personnel in manual operation techniques that did not rely on central servers. Moving forward, the lessons learned from this failed sabotage ensured that the national blood supply remained secure against increasingly sophisticated digital threats, reinforcing the stability of the entire healthcare ecosystem.