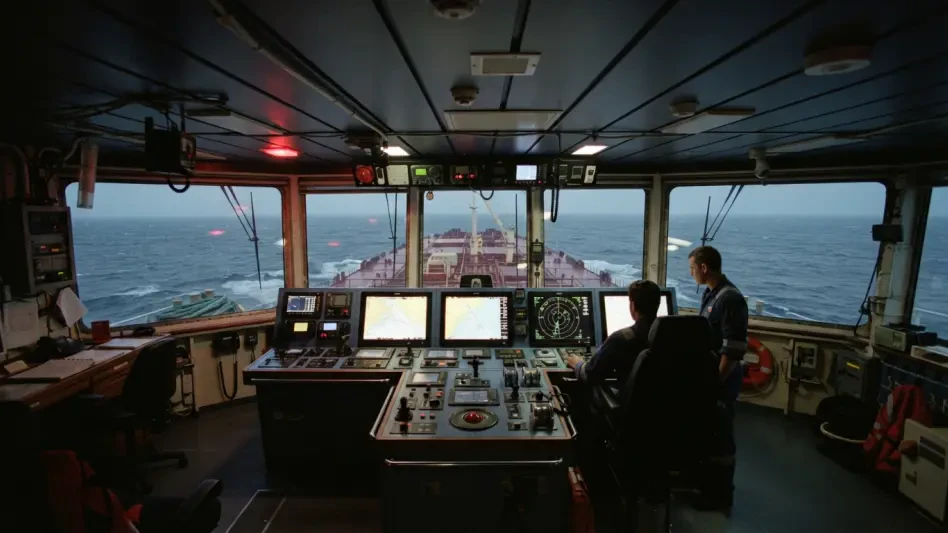
Cyber resilience in the maritime sector depends on treating digital hygiene with the same gravity as physical safety and environmental compliance. As the global shipping industry completes its transition into a fully interconnected digital ecosystem in 2026, the traditional isolation of mechanical ship systems has become a relic of the past. Today, vessels operate as sophisticated floating data centers where information technology (IT) and operational technology (OT) converge to optimize fuel efficiency and voyage planning. However, this connectivity introduces vulnerabilities that technical firewalls alone cannot resolve. Collaborative research from industry leaders indicates that while software updates are vital, the actual frontline of maritime defense remains the behavior of the crew. Data from 2024 suggests that over a quarter of all cyber incidents originated from simple human errors, highlighting a gap between advanced technical security and the daily digital habits of personnel.
Human Vulnerabilities: The Seven Deadly Cyber Sins
The human element is frequently the primary conduit for malicious actors to infiltrate otherwise hardened maritime systems. While technical flaws are often blamed for security breaches, the routine, insecure behaviors of crew members and shore-based staff create the most significant risks. These behaviors, often characterized as the “seven deadly sins” of maritime cyber hygiene, range from financial carelessness to the use of unverified hardware. Because many crew members view cybersecurity as a specialized IT task rather than a personal responsibility, they may inadvertently bypass safety protocols to save time or increase convenience. This disconnect between operational speed and digital safety creates a landscape where approximately 75% of recorded incidents require active crew intervention to mitigate. Consequently, addressing the psychological and behavioral aspects of security is now as critical as deploying the latest encryption tools on vessel servers.
Financial Deception and Unverified Transactions
One of the most persistent threats facing shipping companies involves the manipulation of financial transactions through unvalidated parties. Criminal organizations frequently employ Business Email Compromise (BEC) to deceive shore-based staff or senior officers into redirecting large sums of money. These attackers often monitor communication threads for weeks, waiting for the perfect moment to inject a fraudulent invoice or a request to update bank account details. The sophistication of these scams has reached a point where fraudulent emails are indistinguishable from legitimate correspondence, often using similar domains or compromised official accounts. Without a rigorous, non-digital verification process, such as a direct voice confirmation via a known telephone number, maritime organizations remain highly exposed. The financial impact of a single successful redirection can be catastrophic, potentially disrupting the operational budget of an entire fleet and causing severe long-term damage to vendor relationships.
Risks of Removable Media and Phishing Links
The convenience of portable storage devices continues to be a major conduit for malware, bridging the air gap between general internet-connected systems and critical navigation hardware. Crew members often use personal USB drives or external hard disks to transfer files or media, inadvertently carrying malicious code into the ship’s internal network. When these unscanned devices are connected to safety-critical operational technology, such as the Electronic Chart Display and Information System (ECDIS), the consequences can be immediate. Malware can disable navigation sensors or provide a gateway for remote attackers to gain control over the vessel’s steering. Furthermore, the use of messaging apps for professional communication has expanded the attack surface. A single click on a malicious link within a mobile chat can silently install spyware that eventually migrates to the vessel’s backbone infrastructure, necessitating complex remediation efforts that can take days to complete while at sea.
Operational Security: Protecting Networks from Interference
As vessels become more autonomous, the protection of operational technology becomes the cornerstone of maritime safety. Unlike standard IT systems, OT regulates the physical movements of the ship, including propulsion, ballast management, and power distribution. The convergence of these systems with cloud-based monitoring tools means that an entry point in a secondary system, such as a crew Wi-Fi network, can potentially lead to the engine room. This interconnectedness necessitates a shift toward network segmentation, where critical safety systems are isolated from general-purpose communications. However, even the most robust network architecture can be undermined by unauthorized access or poorly managed third-party connections. Maintaining the integrity of these systems requires constant vigilance and a clear understanding of every device connected to the network. As 2026 progresses, the industry is moving toward a zero-trust model where every connection is verified before access is granted.
Dangers of Shadow Connections and Remote Access
The rise of shadow IT on modern vessels presents a unique challenge to network administrators and ship security officers. In an effort to maintain contact with home, crew members often create unauthorized Wi-Fi hotspots or connect personal laptops directly to vessel network ports. These unauthorized connections effectively create unmonitored backdoors that bypass established security protocols. Because these devices are not managed by the corporate IT department, they often lack necessary security patches, making them easy targets for exploitation. Remote access for maintenance is another critical vulnerability; if access ports are not strictly managed or are left open after a service call, they provide a permanent entry point for hackers. Malicious actors may also impersonate manufacturers to gain entry, using stolen credentials to interfere with propulsion. Failure to secure these pathways poses a direct threat to the vessel’s physical stability and the safety of the global supply chain.
Integrating Resilience into Modern Ship Operations
The integration of cyber resilience into daily maritime operations has moved beyond technical implementation toward a holistic cultural adaptation. Organizations that prioritized the human element effectively reduced their risk profiles by addressing the underlying behavioral patterns that led to system flaws. By implementing rigorous verification for financial transactions and strict management of removable media, shipowners protected their assets from the most common entry points of digital disruption. They also recognized that securing the supply chain required active collaboration with vendors to ensure that third-party access did not compromise vessel integrity. These proactive steps transformed cybersecurity from a reactive IT task into a core component of operational safety and excellence. Moving forward, the industry adopted a standard where digital hygiene was practiced by every crew member, ensuring that the global supply chain remained resilient against the increasingly complex tactics of cyber adversaries.