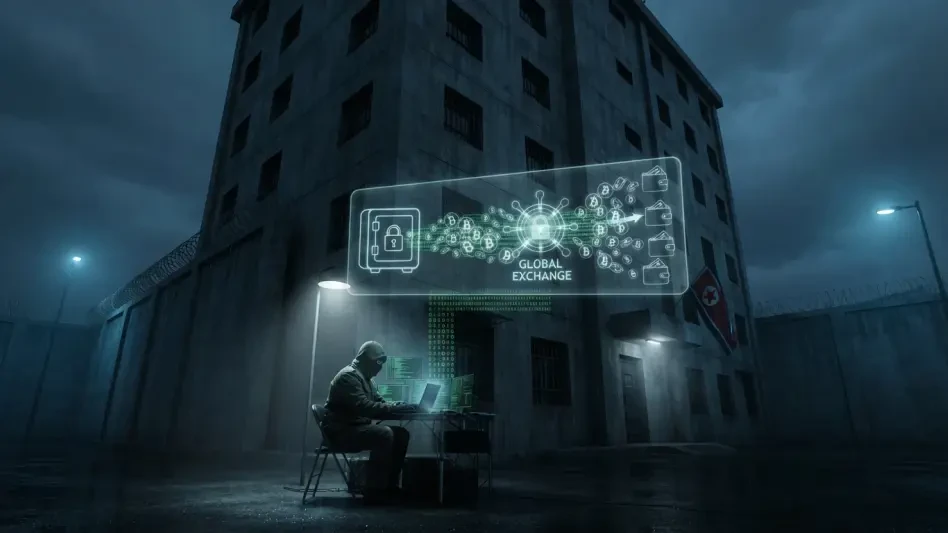
To maintain operational security, the North Korean hacking cells based in China are strictly isolated from one another, ensuring that the exposure of one unit does not compromise the entire network. This specialized infrastructure enabled the unprecedented theft of $6.3 billion from Binance in November 2026, a heist that effectively crippled the stability of the digital asset market overnight. As the world’s largest cryptocurrency exchange, Binance represented the pinnacle of decentralized finance, yet its layered defenses were breached with a level of precision that suggests months of preparation and state-level backing. The immediate financial fallout sent Bitcoin and Ethereum into a tailspin, while geopolitical tensions spiked between Washington and Pyongyang. Analysts have noted that the sheer scale of the extraction required not only technical brilliance but also a sophisticated money-laundering operation to move such a massive sum through various mixers and non-compliant bridges. This event has fundamentally altered the global perception of digital security, forcing a re-evaluation of current defense paradigms across the entire industry.
Political Friction: Official Denials and Internal Truths
While the evidence linking the North Korean regime to the Binance breach became undeniable, the official response from Pyongyang remained one of fierce and indignant denial. Kim Yo-jong, the powerful sister of leader Kim Jong-un, issued several high-profile statements dismissing the accusations as political provocations and preposterous rumors generated by the United States. She framed the global outcry as a targeted attempt to isolate her nation and justify further economic sanctions. However, this public narrative was sharply contradicted by private intelligence gathered from the ground in China’s Liaoning Province. A high-ranking officer within the Reconnaissance General Bureau admitted that the operation utilized the exact signatures and data-routing protocols consistent with the regime’s elite cyber units. This internal discrepancy reveals a deliberate strategy of strategic ambiguity, where the leadership maintains plausible deniability while its operatives celebrate a successful mission.
The discrepancy between the regime’s public facade and its operational reality has sparked a new wave of international skepticism regarding diplomatic engagements with North Korea. South Korean cybersecurity analysts from firms like the Genians Security Center have emphasized that these high-profile hacks are not isolated criminal acts but are essential pillars of the regime’s national budget. By utilizing digital theft as a primary source of foreign currency, the state bypasses traditional financial oversight and sanctions. Experts have noted that the sophistication seen in the Binance incident suggests that the Reconnaissance General Bureau has been training a new generation of hackers specifically for decentralized finance targets since early 2026. This long-term strategic investment ensures that while political leaders offer olive branches or denials on the world stage, their technical units simultaneously execute attacks that undermine global economic stability. The normalization of this two-pronged strategy makes traditional deterrence difficult.
Tactical Execution: The TraderTraitor Playbook
Investigative teams from the FBI and Binance security identified a collective known as TraderTraitor as the primary actor behind the November incident. This group has moved away from traditional brute-force attacks, instead perfecting a social engineering methodology that targets the human element of the security chain. Throughout mid-2026, the hackers posed as executive recruiters and high-level software engineers on professional networking platforms, slowly building rapport with key Binance administrators. They enticed these employees with lucrative job opportunities and technical assignments that appeared entirely legitimate. These assignments required the victims to download modified software or development tools that contained deeply embedded malware. Once the code was executed on a secure workstation, the hackers gained an invisible foothold within the exchange’s internal network. By bypassing firewalls through authenticated employee devices, the attackers were able to extract private keys without triggering the usual threshold alerts.
Beyond initial contact, the technical success of the Binance breach relied on a highly customized variant of malware that remained undetectable by standard antivirus protocols. Once an employee agreed to a technical test, they were directed to a repository that hosted what appeared to be common development libraries or infrastructure management tools. These files contained a dormant secondary stage that would only activate after confirming the host machine was connected to the Binance internal network via a valid virtual private network. Once active, the malware performed a memory scrape to harvest temporary session tokens and cryptographic credentials used by senior administrators. This allowed the TraderTraitor group to simulate legitimate administrative sessions, giving them the ability to authorize massive transfers without secondary verification flags. The elegance of the code lay in its ability to mimic the routine traffic patterns of the company’s own staff, ensuring that the exfiltration of the $6.3 billion appeared as authorized internal movements.
Institutional Architecture: The Future of Cyber Defense
The institutional framework supporting these operations is centered within the Reconnaissance General Bureau, an agency that has evolved into a global powerhouse for cyber warfare. To ensure maximum efficiency and minimal risk, the bureau has deployed approximately 80% of its technical workforce to specialized hubs in China. These operatives are organized into tiny, self-sufficient cells that have no knowledge of each other’s specific targets or geographic locations. This degree of compartmentalization is so extreme that individual units often operate with total autonomy, occasionally leading to internal competition that has even resulted in the hacking of their own state-run financial institutions. This cell structure makes the network incredibly resilient to international law enforcement efforts, as dismantling one team does not provide a path to the others. The Binance heist was a culmination of this decentralized model, where years of refined standardized procedures were deployed simultaneously to drain billions of dollars with clinical efficiency and total secrecy.
The resolution of the Binance crisis demanded a complete reassessment of how global financial institutions approach their defensive perimeters. It was determined that technical safeguards like encryption and multi-factor authentication were no longer sufficient against attackers who specialized in psychological manipulation. Organizations began shifting their focus toward intensive behavioral training programs that taught staff to recognize the sophisticated hallmarks of state-sponsored social engineering. These protocols emphasized the verification of professional contacts and the mandatory sandboxing of all external software assignments in isolated environments. The industry moved toward zero-trust architectures where even authenticated devices were subject to constant behavioral analysis to detect anomalies in real time. Ultimately, the 2026 heist proved that the most critical vulnerability in any system was not the code, but the people who managed it. Security leaders emphasized that long-term survival required a culture of perpetual skepticism and rigorous interpersonal verification.