Digital security has historically relied on the assumption that a physical device in a user’s pocket serves as a reliable proxy for identity, but recent systemic failures have shattered this long-standing confidence. While the industry previously championed SMS-based multi-factor authentication as a major improvement over simple passwords, the landscape in 2026 demands a far more rigorous approach to protecting sensitive data. The Cybersecurity and Infrastructure Security Agency has issued definitive guidance that effectively demotes text-based verification to a last-resort status. This shift is prompted by the realization that mobile networks were never designed to be secure channels for cryptographic secrets. As attackers increasingly bypass these legacy systems, the gap between perceived safety and actual vulnerability continues to widen for organizations and individuals alike. Moving forward, the conversation must transition from basic two-step verification toward advanced, phishing-resistant methods that can actually withstand modern interception techniques.
Structural Flaws in Mobile Network Security
The Vulnerability of Cellular Infrastructure
A significant catalyst for the recent re-evaluation of SMS-based security was the Salt Typhoon campaign, which demonstrated the alarming reach of state-sponsored actors within domestic telecommunications infrastructure. This sophisticated hacking operation, linked to specific foreign intelligence agencies, successfully compromised multiple United States telecom providers, granting attackers deep access to the core of the messaging environment. By gaining control over these networks, adversaries were able to intercept unencrypted communications, including the very login codes intended to secure sensitive accounts. This level of access effectively rendered traditional multi-factor authentication useless, as the one-time passwords were stolen before they ever reached the intended recipient’s device. The incident served as a stark reminder that even the most disciplined users cannot defend against threats that originate within the delivery mechanism itself, making the inherent insecurity of the cellular backbone a primary concern for national security experts.
Risks of Number Porting and Routing
Beyond the threat of direct network compromise, traditional SMS authentication remains plagued by structural weaknesses that have been known to the security community for years, yet persist due to the inertia of legacy systems. One of the most prevalent methods involves SIM swapping, where an attacker utilizes social engineering or insider access at a mobile carrier to transfer a target’s phone number to a new device under their control. Once the number is ported, all incoming authentication codes are delivered directly to the criminal, providing them with unrestricted access to banking and social media accounts. Furthermore, the global telecommunications routing system, known as Signaling System No. 7, contains legacy vulnerabilities that allow sophisticated actors to redirect messages remotely without the user ever knowing their data has been intercepted. These protocol-level flaws are nearly impossible for a standard consumer to mitigate, as they exist within the fundamental architecture of how mobile calls and messages are routed across international borders.
Modern Standards for Identity Protection
Implementing Phishing-Resistant Hardware Keys
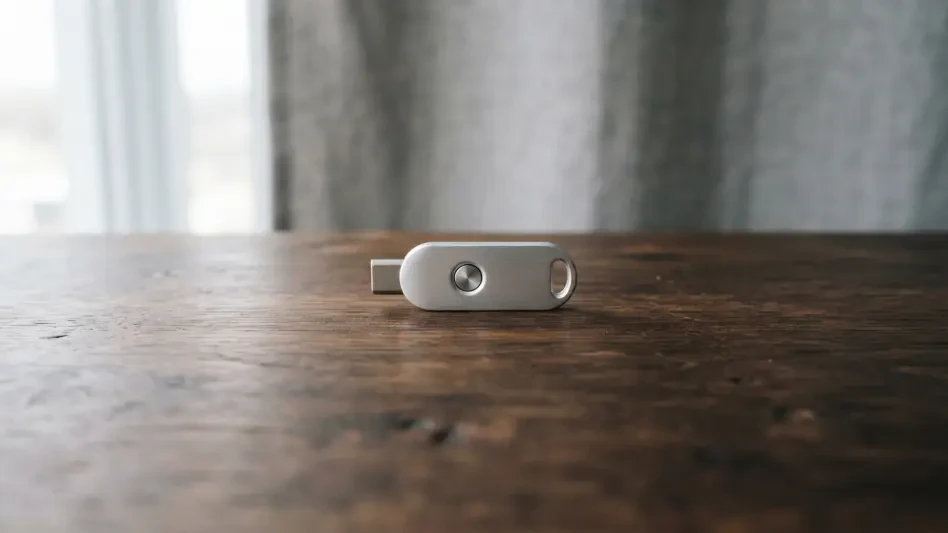
The gold standard for modern identity protection has shifted toward phishing-resistant technologies, specifically those built on the FIDO and WebAuthn standards, which offer a fundamentally different security model. Unlike SMS codes or even mobile authenticator apps, these tools verify the legitimacy of a specific website through a cryptographic handshake before providing any credentials. This mechanism ensures that even if a user is tricked into visiting a fraudulent login page, the hardware security key or passkey will refuse to authenticate, effectively neutralizing the threat of phishing. While authenticator apps that generate time-based codes are still considered a significant improvement over SMS—primarily because they do not rely on the vulnerable cellular network—they can still be compromised if a user is coerced into entering a code on a malicious site. By moving toward physical keys or device-based passkeys, organizations and individuals can create a security posture that is not only more robust but also vastly more resilient against the automated attack patterns common in 2026.
Executing a Strategic Migration Plan
To address these systemic risks, the focus shifted toward a tiered strategy that prioritized the most critical entry points, such as primary email addresses and financial portals. Security professionals recommended that users first establish their digital identity anchors by implementing hardware keys or passkeys on their most sensitive accounts. Once these phishing-resistant foundations were in place, the secondary step involved removing phone numbers as a recovery option to prevent attackers from using SIM swapping as a backdoor. This proactive approach ensured that even if a mobile device was lost or a carrier account was compromised, the core digital identity remained shielded by stronger cryptographic barriers. Ultimately, the transition away from SMS was recognized not as an abandonment of convenience, but as a necessary adaptation to an environment where old methods no longer provided sufficient protection. These actions provided a clear roadmap for securing digital lives against the sophisticated interception techniques that were common.