The realization that a single administrative oversight could dismantle the security of five hundred distinct corporate networks simultaneously has fundamentally reshaped the way global telecommunications providers perceive their digital perimeters. In the complex architecture of modern IT, the management layer was long considered a sanctuary, a secure cockpit from which an entire fleet of firewalls and servers could be safely steered. However, the events surrounding the 2024 exploitation of the Fortinet ecosystem shattered this complacency. Security professionals found that the very tools designed to simplify network administration were the primary vectors for a level of access that surpassed the most aggressive external attacks. This vulnerability highlighted a systemic flaw: when the management platform is compromised, the entire security perimeter ceases to exist.
The significance of this breach extends far beyond a single software patch or a temporary service disruption. It represents a paradigm shift in threat actor strategy, where the focus moved from the individual workstation to the infrastructure hub. For a Managed Service Provider (MSP), the stakes are existential. A compromise at this level does not just leak internal data; it grants an adversary the keys to every client network under their supervision. As organizations look toward the period from 2026 to 2030, the lessons of the Peerstitch intrusion serve as a definitive guide for defending against the next generation of infrastructure-level threats. Understanding how this malware bypassed sophisticated defenses is essential for anyone tasked with maintaining the integrity of distributed networks.
The Invisible Threat Within the Network Hub
For decades, the concept of a “secure perimeter” focused on hardening the walls of the castle, but the Peerstitch incident proved that the most dangerous enemies are those who already possess the keys to the gate. The modern enterprise relies on centralized management systems to maintain consistency and security across vast geographical distances. While these systems offer operational efficiency, they also create a singular point of failure that is incredibly attractive to sophisticated adversaries. When the management layer is exploited, the intruder gains the same administrative powers as the legitimate staff, allowing them to move through the network without triggering the alarms that typically follow a brute-force entry.
The exploitation of the Fortinet ecosystem in 2024 served as a harsh wake-up call for the industry. This was not a standard phishing attack or a localized server breach; it was a surgical strike against the management plane itself. By targeting the software used to oversee thousands of firewalls, the attackers bypassed the traditional security stacks that monitor traffic between the internet and the internal network. This demonstrated that trusting the management layer without additional layers of verification is a dangerous liability. In a world where edge devices are the first line of defense, the compromise of the platform that controls them is nothing short of catastrophic.
The psychological impact on the cybersecurity community was profound, as it forced a transition from a posture of trust to one of constant verification. The management hub, once thought of as a fortress, was revealed to be a high-velocity delivery mechanism for malicious intent. This shift required a fundamental rethink of how administrative credentials and management protocols are handled. It became clear that if an attacker could masquerade as the management console, every downstream device would follow its instructions, whether those instructions were to update firmware or to open a backdoor for data exfiltration.
The Strategic Shift Toward Edge Management Targets
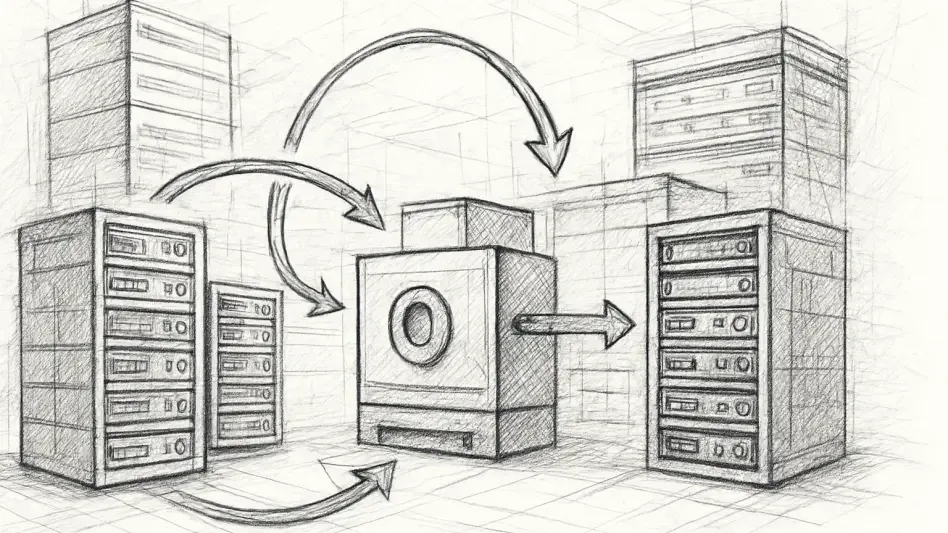
The “hub-and-spoke” vulnerability has become the centerpiece of modern cyber-warfare, where compromising one central manager is far more efficient than breaching 500 individual corporate networks. Adversaries have recognized that the return on investment for a single management-level breach is unparalleled. Instead of spending months navigating the defenses of a single corporation, they can now gain access to the entire portfolio of a Managed Service Provider in one fell swoop. This efficiency allows threat actors to scale their operations at a rate that was previously impossible, making MSPs the ultimate gateway for large-scale intelligence gathering and economic espionage.
The emergence of CL-STA-0954, the sophisticated actor identified behind the Peerstitch intrusion, highlights the level of expertise now being directed at these hubs. This group did not merely use off-the-shelf tools; they demonstrated an intimate understanding of specific vendor architectures and management protocols. Their approach was methodical, focusing on the infrastructure that connects disparate networks rather than the networks themselves. This strategic shift suggests that nation-state intelligence agencies are increasingly viewing MSPs not just as targets, but as infrastructure that can be co-opted to serve their broader strategic objectives.
By leveraging the inherent trust between an MSP and its clients, these actors can remain undetected for months. They do not need to generate noisy traffic or use aggressive exploits once they have secured a foothold in the management platform. Instead, they “live off the land” using the provider’s own tools to monitor traffic, harvest credentials, and map out the internal structures of client organizations. This type of intrusion is particularly difficult to detect because the malicious activity is blended with legitimate administrative tasks, making it nearly invisible to traditional monitoring solutions.
Anatomy of the Peerstitch Intrusion: From Exploitation to Exfiltration
The initial entry into the provider’s network was achieved through the exploitation of CVE-2024-47575, a critical vulnerability that allowed the registration of rogue virtual devices within the management platform. Once the attackers successfully introduced their unauthorized device into the FortiManager ecosystem, they gained the ability to pull comprehensive configuration archives from hundreds of managed firewalls. These archives were not just lists of rules; they were the crown jewels of the network, containing IP addresses, topology maps, and the cryptographic keys used to secure communication. With this information, the attackers had a complete blueprint of the target’s entire digital infrastructure.
Following the extraction of these archives, the actors transitioned into a phase of active reconnaissance. They pushed “sniffer” configurations to downstream firewalls, turning the very tools used for network diagnostics into surveillance instruments. This allowed them to intercept unencrypted HTTP traffic, as well as LDAP and RADIUS queries, which are the lifeblood of corporate authentication systems. By capturing these packets, the attackers could harvest clear-text credentials and session tokens, providing them with the means to move laterally into client environments with legitimate, albeit stolen, identities.
The second stage of the attack utilized CVE-2025-61624 to escalate privileges through a path traversal vulnerability in the system’s auto-script functionality. This served as the delivery mechanism for Peerstitch, a highly advanced ARM64 memory-resident malware injector. Unlike traditional malware that leaves traces on the hard drive, Peerstitch operates entirely within the system’s RAM, making it invisible to file-based antivirus software. It hooks into legitimate host processes to create a covert communication tunnel, allowing the attackers to maintain a command-and-control channel that appears to be routine network traffic. This level of technical sophistication ensures that the malware can survive even if the initial vulnerability is patched.
Expert Perspectives on Advanced Threat Actor Tradecraft
Insights from Palo Alto Networks’ Unit 42 reveal that the Peerstitch campaign represented a masterclass in “living off the land” at the architectural level. Rather than introducing a suite of noisy hacking tools, the actors repurposed the existing capabilities of the compromised firewalls. They used built-in diagnostic commands and legitimate scripting engines to perform their tasks, ensuring that their presence did not trigger anomaly detection systems. This tradecraft demonstrates a level of operational security that is typically associated with top-tier intelligence agencies, emphasizing the seriousness of the threat facing modern service providers.
The attackers also demonstrated a rigorous commitment to anti-forensics, going to great lengths to degrade the quality of system telemetry. They manually suppressed logging services before executing their most sensitive commands and proactively deleted crash logs that might have indicated a failed injection attempt. By intentionally degrading the management tunnel’s performance, they also limited the amount of real-time data that reached the central monitoring consoles. This “blinding” of the security team allowed the actors to work in a low-visibility environment, significantly extending their dwell time within the network.
A consensus among the FBI and the U.S. Secret Service indicates that the “FortiBleed” campaign is part of a broader trend of targeting internet-facing management interfaces. These agencies have observed a sharp increase in the use of harvested credentials and infrastructure exploits to gain access to critical gateways. The focus has moved away from the endpoint and toward the edge, where a single vulnerability can provide a high-yield payoff for the attacker. This collective expert opinion suggests that the industry must move beyond reactive patching and toward a model of proactive, behavioral monitoring of the management plane.
Hardening the Infrastructure: Strategies for MSP Resilience
The resolution of the Peerstitch crisis required more than simple software updates; it necessitated a “High-Gravity” incident protocol that assumed the entire network was compromised. Once a management hub was breached, every downstream device was treated as a potential carrier of the infection. This led to a massive effort to move beyond surface-level remediation. Security teams recognized that the cryptographic integrity of the network had been shattered, and only a complete overhaul of the trust infrastructure could restore safety to the environment.
A rigorous secret rotation framework was established as the primary line of defense. This involved the immediate replacement of all administrative credentials, public certificates, and, most crucially, the private keys used for secure management tunnels. By rotating these secrets, administrators effectively invalidated the data the attackers had exfiltrated during the early stages of the breach. Furthermore, the implementation of Zero Trust architectures for management interfaces ensured that even if a platform was compromised, the ability of an attacker to move laterally would be severely restricted through isolated management channels and multi-factor authentication.
The focus eventually shifted toward next-generation monitoring that prioritized anomalous inter-process memory activity over traditional file signatures. Since Peerstitch lived entirely in memory, detection depended on identifying unusual behaviors within legitimate system processes. Monitoring tools were reconfigured to alert on unexpected script execution and unauthorized changes to the system’s process tree. These proactive measures, combined with a newfound skepticism of management-level trust, allowed service providers to rebuild their infrastructures with a resilience that prioritized visibility and verification above all else. In the end, the industry learned that the price of centralized efficiency was a requirement for decentralized, vigilant security.