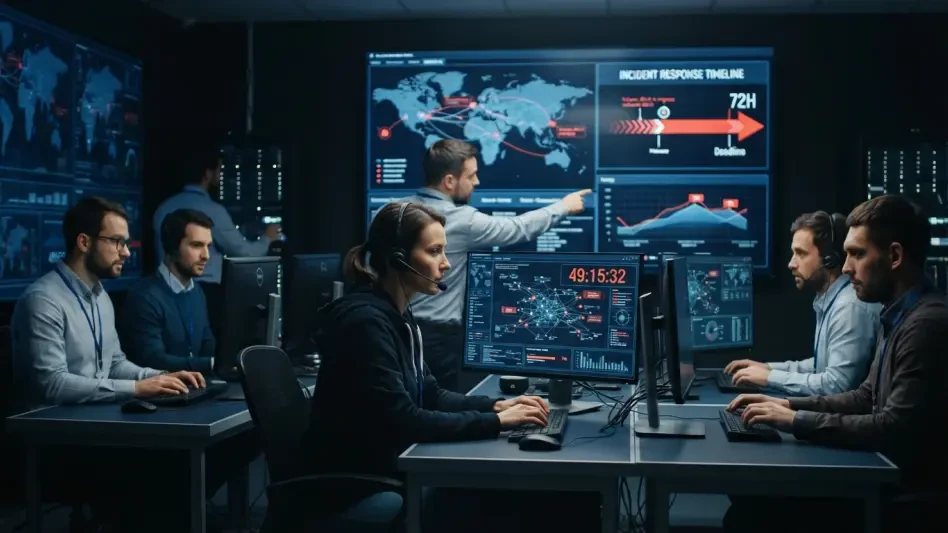
For manufacturers of digital products, the Cyber Resilience Act mandates notification within 24 hours of discovering an actively exploited vulnerability. This requirement represents a tectonic shift in the cybersecurity landscape, moving the industry away from the era of leisurely forensic investigations toward a period of immediate, legally mandated transparency. In the current environment of 2026, the luxury of waiting for complete certainty before informing regulators has vanished, replaced by a “golden hour” mentality where the first three days determine the survival of the enterprise. Organizations are now forced to operate on dual tracks, where technical remediation efforts must run in perfect synchronization with legal disclosure obligations. This compression of time has redefined the role of the Chief Information Security Officer and elevated cybersecurity from a technical concern to a primary fiduciary duty for every board member. As global regulatory bodies align their expectations, the ability to communicate accurately under extreme pressure has become the ultimate benchmark of corporate resilience.
The European Union’s Multi-Layered Regulatory Grid
Expanding Accountability Through NIS 2 and DORA
The Network and Information Security Directive 2, known as NIS 2, has fundamentally restructured how critical infrastructure entities across Europe handle the immediate aftermath of a digital breach. By implementing a mandatory two-stage reporting process, the directive ensures that national authorities are informed of “significant” incidents almost as soon as they are detected. The initial early warning, which must be submitted within 24 hours of awareness, is designed to provide a high-level snapshot of the threat, allowing for cross-border coordination even before the full scope of the damage is understood. This is followed by a detailed incident notification within 72 hours, which requires a more thorough analysis of the cause and the potential impact. This tiered approach prevents organizations from burying incidents in long-term internal reviews and forces a level of operational readiness that was previously seen only in the most advanced security teams.
Building upon this foundation, the Digital Operational Resilience Act, or DORA, has introduced even more stringent timelines for the financial services sector, where systemic stability is the primary concern. Under DORA, financial institutions must report major ICT-related incidents to their respective regulators within 24 hours of discovery, with a mandatory intermediate report following at the 72-hour mark. This framework moves the focus beyond simple data protection to “operational resilience,” meaning companies must demonstrate their ability to maintain essential services during a crisis. Similarly, the Cyber Resilience Act ensures that product manufacturers cannot overlook vulnerabilities in their software or hardware. By requiring a 24-hour notification for actively exploited flaws, the CRA forces companies to maintain a constant state of vigilance, effectively bridging the gap between product development and ongoing security operations in an interconnected marketplace.
Personal Liability for Corporate Leadership
A defining characteristic of the European regulatory shift is the transition from corporate-level penalties to the potential for personal liability for individual leaders. Under the current frameworks of NIS 2 and DORA, management bodies and board members are directly responsible for the implementation and oversight of cybersecurity risk management measures. This change has ended the era where cybersecurity could be treated as an isolated IT problem to be delegated without further inquiry. In several jurisdictions, senior executives now face substantial personal fines, sometimes reaching as high as €5 million, if it is proven that they failed to provide adequate oversight or ignored credible warnings about security deficiencies. This personalization of risk has significantly altered boardroom dynamics, making cyber resilience a recurring and high-priority agenda item that demands deep technical understanding from every director.
This heightened accountability has also led to the adoption of the “credible challenge” standard, where directors are expected to actively interrogate management’s security decisions rather than merely approving them. This shift requires boards to be equipped with the knowledge to ask probing questions about encryption standards, incident response readiness, and the security of the third-party supply chain. Furthermore, the legal pressure has prompted a widespread redesign of internal reporting lines, often resulting in the Chief Information Security Officer having a direct and frequent reporting path to the Chief Executive Officer or the Board of Directors. By tying personal financial and professional reputations to the company’s digital security posture, the EU has effectively ensured that cybersecurity is integrated into the core of the corporate governance structure, fostering a more proactive and resilient organizational culture.
The United States: Materiality and Enforcement
SEC Disclosure Rules and Materiality Assessments
In the United States, the Securities and Exchange Commission has maintained a rigorous focus on the concept of “materiality” to ensure that investors are informed of significant digital risks. Public companies are required to make a determination regarding the materiality of a cyber incident “without unreasonable delay,” a standard that effectively synchronizes with the global 72-hour reporting trend. Once an incident is deemed material—meaning there is a substantial likelihood that a reasonable investor would consider the information important—the company must file an Item 1.05 Form 8-K within four business days. The complexity of this rule lies in the fact that the materiality assessment must often occur while technical investigations are still in their infancy. Management must weigh financial costs, reputational damage, and operational disruptions in real-time, creating a high-pressure environment where legal and technical teams must speak the same language.
The challenge of meeting these requirements has necessitated a more integrated approach to corporate disclosure, where legal counsel is embedded within the incident response team from the very first hour. This integration ensures that the “materiality clock” is monitored constantly, preventing the “unreasonable delays” that have drawn significant scrutiny from federal regulators. Companies have learned that waiting for a perfect forensic report before making a disclosure decision is a risky strategy that can lead to aggressive enforcement actions. Instead, the modern standard involves making iterative assessments based on the best available information at each 24-hour interval. This dynamic disclosure process helps maintain market transparency while providing the company with a defensible record of its decision-making process, which is essential for surviving the inevitable regulatory audits that follow a significant cyber event.
Regulation S-P and the Supply Chain
The recent amendments to Regulation S-P have extended the reach of federal oversight deep into the third-party supply chain, creating a web of accountability for financial institutions. These entities are now mandated to ensure that their service providers maintain robust security protocols and, crucially, notify them of any breach involving sensitive customer data within 72 hours. This requirement has fundamentally changed the nature of vendor management, as institutions can no longer rely on generic security questionnaires. Instead, they must include specific, time-sensitive reporting triggers in their service level agreements to ensure they can meet their own regulatory obligations. This ripple effect means that a security failure at a minor software provider can quickly escalate into a major compliance issue for a large financial institution, requiring a coordinated response across multiple organizations.
Beyond the immediate vendor notification, Regulation S-P requires covered institutions to notify affected individuals as soon as practicable, but no later than 30 days after a compromise has been confirmed. This timeframe puts immense pressure on the initial 72-hour investigation, as the company must accurately identify the scope of the data breach to prepare for public notification. The focus on supply chain integrity has led to the widespread adoption of automated monitoring tools that track vendor security in real-time, allowing institutions to detect anomalies before a breach is even confirmed. By mandating transparency throughout the vendor ecosystem, the SEC and other regulators have effectively forced a higher standard of security across the entire digital economy, ensuring that no single link in the chain becomes a silent point of failure for the broader financial system.
Aggressive Federal Oversight and Enforcement
The SEC has clearly signaled that its enforcement priorities in 2026 are centered on operational resiliency and the emerging risks associated with Artificial Intelligence. Examination teams are now specifically looking at how companies utilize AI both for defense and as a potential attack vector, requiring organizations to demonstrate that they have accounted for these risks in their incident response plans. Ransomware remains a top priority, but the focus has shifted from the payment itself to the underlying safeguards that were in place before the attack. Regulators are increasingly penalizing companies for deficiencies in basic security hygiene, such as the absence of multi-factor authentication or the failure to conduct regular employee training. These failures are now viewed as actionable violations of Regulation S-P, regardless of whether they were the primary cause of a specific breach.
This aggressive stance is reflected in recent enforcement actions where the SEC has scrutinized the “safeguards” of institutions long before an incident occurs. Deficiencies in risk assessment processes and inadequate documentation of incident response drills are now sufficient grounds for significant penalties. The message from federal authorities is clear: compliance is not a reactive exercise that begins after a breach, but a continuous obligation to maintain a defensible security posture. This environment has prompted companies to invest heavily in “regulatory-ready” security stacks that provide immutable logs and clear audit trails of all security decisions. By focusing on the structural health of an organization’s security program rather than just the outcome of a single incident, the government is driving a more systemic improvement in the nation’s overall cyber defense capabilities.
Strategic Realities of Compressed Timelines
Moving from Technical Recovery to Regulatory Readiness
The transition from a primary focus on technical recovery to a dual focus on technical and regulatory readiness has required a complete overhaul of traditional incident response playbooks. In the current 72-hour paradigm, organizations must have pre-drafted notification templates and pre-approved communication plans ready for immediate deployment. The quality of a company’s documentation is now its most critical defense against future litigation and regulatory fines. Regulators expect to see a chronological record that details exactly when an incident was first detected, when it was escalated to senior management, and the specific data points that informed the materiality assessment. This level of detail requires the use of automated incident management platforms that can capture every action taken by the response team in a format that is easily digestible for legal and regulatory review.
To achieve this level of readiness, organizations have moved away from static PDF documents toward interactive response systems that guide teams through the necessary legal steps in real-time. These systems ensure that no mandatory notification windows are missed and that all internal stakeholders are kept informed through automated dashboards. The emphasis is no longer just on “fixing the problem” but on “managing the event” in a way that satisfies both internal operational needs and external legal requirements. This shift has also led to the inclusion of external legal counsel and strategic communications experts in the initial response team, ensuring that every technical decision is weighed against its potential impact on public disclosure and regulatory standing. Documentation has become the primary mechanism for proving that a company acted with “due care” under the intense pressure of the clock.
Stress Testing and Rapid Escalation Protocols
Static response plans have proven insufficient for the speed of modern threats, leading to the widespread adoption of high-frequency, privileged tabletop exercises. These simulations are no longer just technical drills for IT staff; they are complex “paper drills” that involve the CEO, the board, and legal counsel. The goal of these exercises is to simulate the pressure of making high-stakes disclosure decisions while forensic facts are still emerging and incomplete. By practicing these scenarios, management teams can identify gaps in their escalation protocols and ensure that information moves from the security operations center to the boardroom without delay. These stress tests help build the “muscle memory” required to handle a 24-hour early warning or a 72-hour notification without succumbing to the chaos that often accompanies a major cyber event.
Rapid escalation protocols are now typically triggered by specific “high-impact” indicators, such as the detection of a ransomware strain, evidence of unauthorized access to sensitive databases, or a significant disruption to customer-facing services. These triggers bypass traditional bureaucratic layers, ensuring that the legal and executive teams are alerted immediately. This immediate involvement is crucial for the “materiality” clock, as it allows the legal team to begin their assessment concurrently with the technical investigation. Companies that have successfully navigated major incidents in 2026 have almost universally credited their success to these rapid escalation paths. By eliminating the friction in internal communication, organizations can ensure that they meet their global reporting obligations while still providing their technical teams with the space needed to contain and remediate the threat.
Evolution Toward Resilience
Organizations that survived the initial implementation of the 72-hour rule prioritized the integration of technical and legal reporting. They established comprehensive monitoring systems that allowed for the rapid identification of reportable incidents and fostered a culture where transparency was valued over silence. Management teams learned that the “credible challenge” standard required them to be more engaged in security oversight than ever before, leading to the creation of specialized board committees focused exclusively on digital risk. These enterprises moved beyond simple compliance and instead built operational resilience into their core business processes, ensuring that they could withstand both the technical impact of a breach and the ensuing regulatory scrutiny. The transition was difficult, but it resulted in a more robust and transparent global digital economy.
The shift toward rapid accountability also compelled companies to rethink their relationships with third-party vendors and service providers. They updated their procurement processes to include rigorous security evaluations and enforced strict notification timelines in every contract. This proactive approach allowed them to manage supply chain risks more effectively and ensured that a single vendor’s failure would not lead to their own regulatory non-compliance. Ultimately, the industry moved away from treating cybersecurity as a series of isolated events and toward seeing it as a continuous, managed risk. The lessons learned during this period demonstrated that the ability to react quickly and communicate clearly was the most effective way to maintain investor confidence and protect long-term corporate value in an increasingly volatile digital landscape.